A contract is asking for CMMC. We tell you where you really stand.
Start with a directional estimate of your SPRS self-assessment score. We help verify your scope, close gaps, and prepare evidence. Castile handles readiness; an independent assessor handles certification.
You've probably said one of these
- "A prime just put CMMC language in our contract and I don't have an answer."
- "Someone handed me this on top of my actual job."
- "I don't know if we're a Level 1 or a Level 2, or what's even in scope."
- "I don't know what our SPRS score would even be."
- "I keep seeing CMMC updates and do not know what applies to us."
- "I'm scared of reporting a score we can't back up."
Start by understanding your scope, your evidence, and what applies to your contract.
See your estimated score before you talk to anyone
A few targeted questions, no access to your systems, a directional SPRS estimate in minutes.
Use the estimate to identify questions for your readiness conversation. It is not a verified assessment or a score to submit as evidence. The paid Snapshot checks your actual environment.
What it checks
- Plain-English questions about your systems, data, and current controls.
- A directional SPRS estimate based on your answers.
- No system access. The questionnaire does not inspect your environment or replace an assessment.
 CMMC Methodology
We are the advisor, not the certifier
That separation is by design.
The first four steps are ours. The last one never is, and that boundary is what keeps your assessment independent.
We prepare the gap assessment, System Security Plan, documentation, and evidence. When third-party assessment is required, an accredited assessor performs that independent review.
You get a documented readiness position and a clear handoff, without a promise of certification.
CMMC updates
Check the latest guidance before you plan.
The July 13, 2026 announcement suspended the Phase II rollout. The official program page continues to describe implementation as paused in Phase 1. Check the latest official guidance and your contract requirements before deciding which assessment path applies.
Your next step: confirm your scope, keep your security evidence current, and review applicable requirements with your contracting officer.
Status summary dated October 15, 2026. Follow the official links for subsequent changes.
What we usually find
Gaps can include the System Security Plan, logging, training records, and encryption evidence. We check existing controls and documentation before recommending changes.
Start with scope. Identify the people and systems that handle controlled information, then define the assessment boundary. A clear boundary helps avoid unnecessary work.
A recent engagement
A defense contractor came to us with no clear read on where they stood. The assessment found real, fixable gaps, including one finding that led to an immediate fix the same week. A roadmap gave them a clear next 60 days.
“It wasn't as bad as I expected, but it was still bad, and knowing exactly where we stood was worth it.”
Jeremy Teeples, COO, Qal-Tek Associates
Every engagement ends in an answer, not a shrug
| Snapshot | Readiness Roadmap | Guided Readiness | |
|---|---|---|---|
| Timeline | Two weeks from access to a clear answer | Snapshot timeline, plus the mock assessment | Runs alongside your remediation; set at kickoff |
| Access required | Read-only, for the Snapshot period | Same as Snapshot | Same, plus check-ins through implementation |
| Deliverables | Your scope, level, and hard blockers, in writing | Everything in Snapshot, plus a full mock assessment against all 110 requirements, a gap register, and a costed effort estimate | Everything above, plus your System Security Plan, action plans, a complete policy set, and a re-check before the real assessment |
| Best for | A fast, honest answer before you commit further | Budgeting and planning the work ahead | Wanting Castile hands-on through the fix, not just the diagnosis |
| What happens next | The fee applies in full if you go further within 90 days | You decide whether to self-remediate or bring us in | A re-check, then the accredited assessor |
Each tier documents your readiness position, remaining gaps, and the work ahead. The free score is only an estimate; the Snapshot verifies your environment. Readiness work is not certification.
See it before you commit to it
Every Guided Readiness engagement includes a live dashboard like this one, built the same way and updated as the work happens. This is the real tool, running on fictitious data.
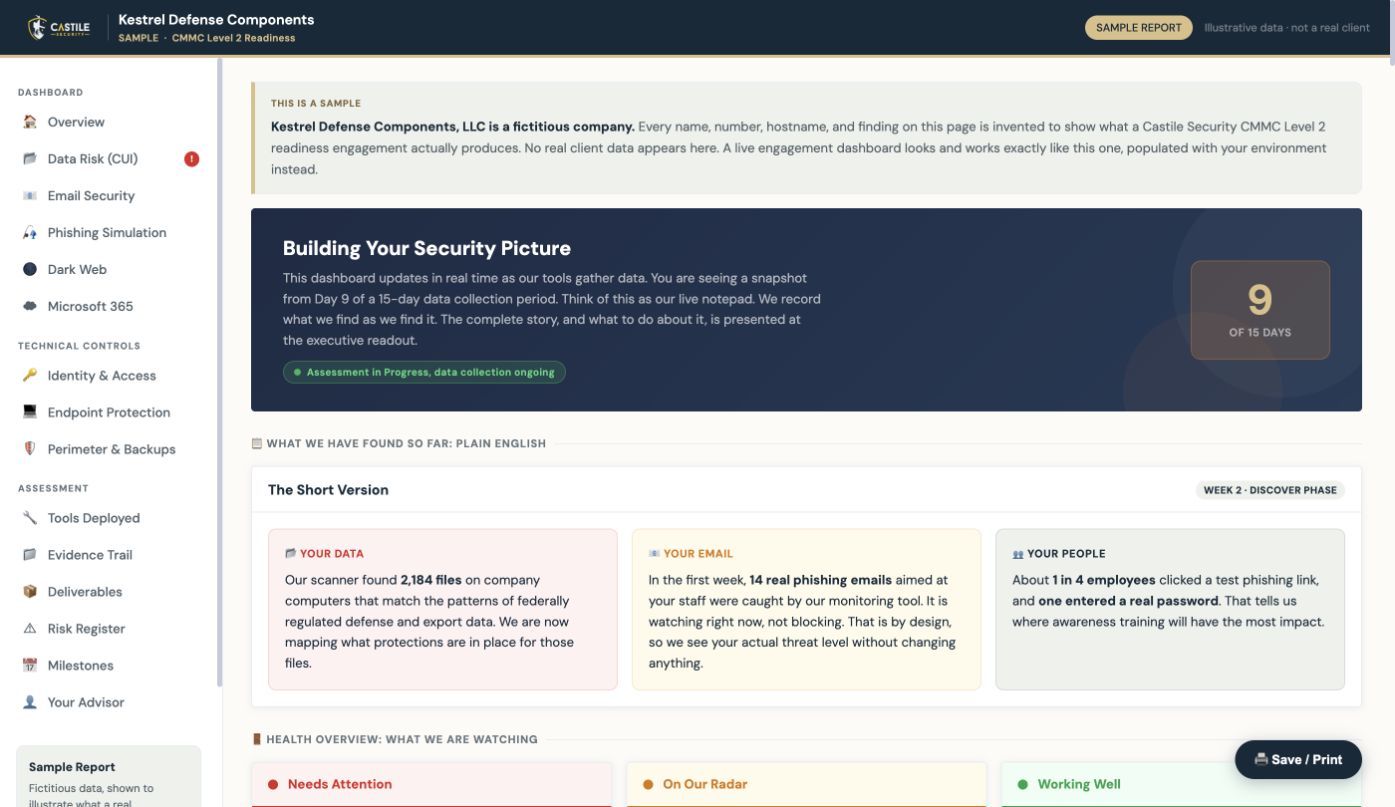 Open the live sample dashboard →
Fictitious company, real methodology. No client data appears anywhere in this sample.
Written guarantees, every engagement
Scope
On a CMMC engagement, if an assessor raises an in-scope requirement we did not assess, we assess it, document it, and advise on it at no charge.
Schedule
A missed milestone within our control earns you a credit.
Findings
On a first Snapshot, if we find nothing material you did not already know, you do not pay for it.
We will never guarantee a certification outcome or a score. Anyone who does is guaranteeing something they do not control.
Questions
What does the free score actually measure?
A directional estimate of where your SPRS self-assessment score would land today, based on how you answer a handful of plain-English questions. It is a starting point, not a substitute for the Snapshot, which verifies it against your actual environment.
What level do we actually need?
It depends on the contract language and what controlled information you touch. The Snapshot answers this directly, usually within two weeks.
We don't know our scope. Is that normal?
Yes. Almost nobody arrives knowing their real scope. Finding it, and usually shrinking it, is the first thing we do.
How do we keep up with changing CMMC requirements?
Start with the official CMMC program page and the requirements in your solicitation or contract. Rollout announcements do not replace a review of your scope, applicable clauses, and assessment obligations. Our CMMC updates section links to the official sources.
Will Castile certify us?
No, and that is deliberate. We do the readiness work. An accredited third-party assessor does the certifying. That separation is what keeps the assessment independent.
Do you work with our existing IT provider?
Yes. Keep them. They keep the systems running; we handle the CMMC-specific gap work and documentation alongside them.
Do you work in Spanish?
Sí. Several of our contractor clients run their engagement with us in Spanish.
Know where you stand before the assessor tells you.
Already have your free score? Bring it to the Readiness Review and we'll confirm the level, map the gaps, and give you a prioritized path to close them.